Document Management
Your documents are everywhere. That means they are nowhere.
Esii DDMS brings all your enterprise documents into a single, access-controlled view, your NAS drives, AWS S3 buckets, Microsoft Azure Blob and Windows File Server, without migrating a single file. Every file is governed, every access is logged and every share carries an expiry.
Documents are your most used asset. Also your least governed one.
Files shared over email, stored on personal drives and accessed without any record. DDMS brings order without disrupting how teams work.
Critical documents live across email threads, personal OneDrive folders, shared drives and USB sticks. Version control is a manual exercise that no one follows.
A sensitive contract is shared externally. No one knows who forwarded it, who opened it or when. Compliance and legal teams have no evidence chain.
Teams that collaborate need to share documents. But sharing without governance, expiry controls & access logs creates a permanent security exposure.
Connect what you already have.
Govern it from one place.
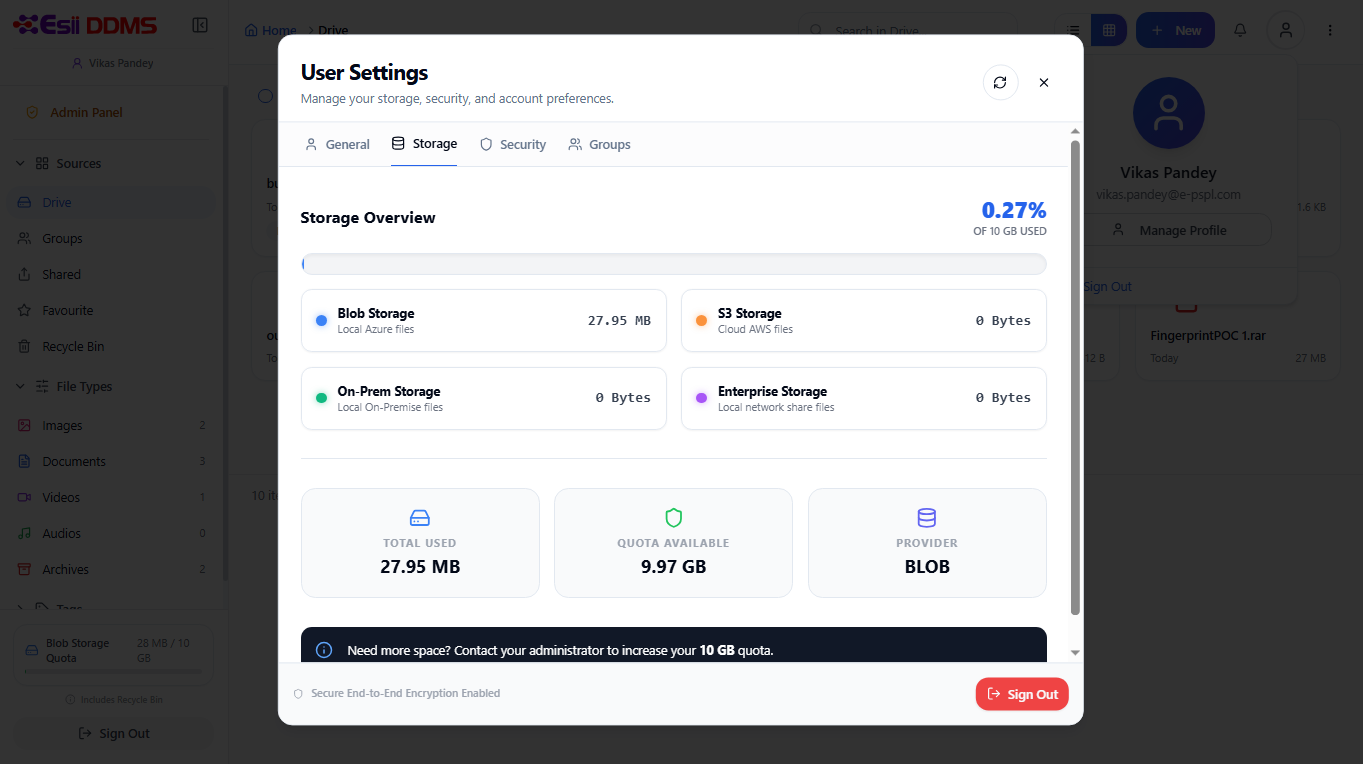
DDMS connects directly to your existing NAS, Windows File Server, AWS S3 and Azure Blob storage. Your files remain where they are. No migration required.
1. Connect your existing storage
Administrators configure connections to your on-premise NAS, AWS S3 buckets, Azure Blob containers or Windows File Server. Files stay in their current location.
2. Apply access at folder & file level
Role-based policies via Microsoft Entra ID, Google Workspace or local authentication decide who can upload, view, download, delete or share, down to the file.
3. Monitor every action in real time
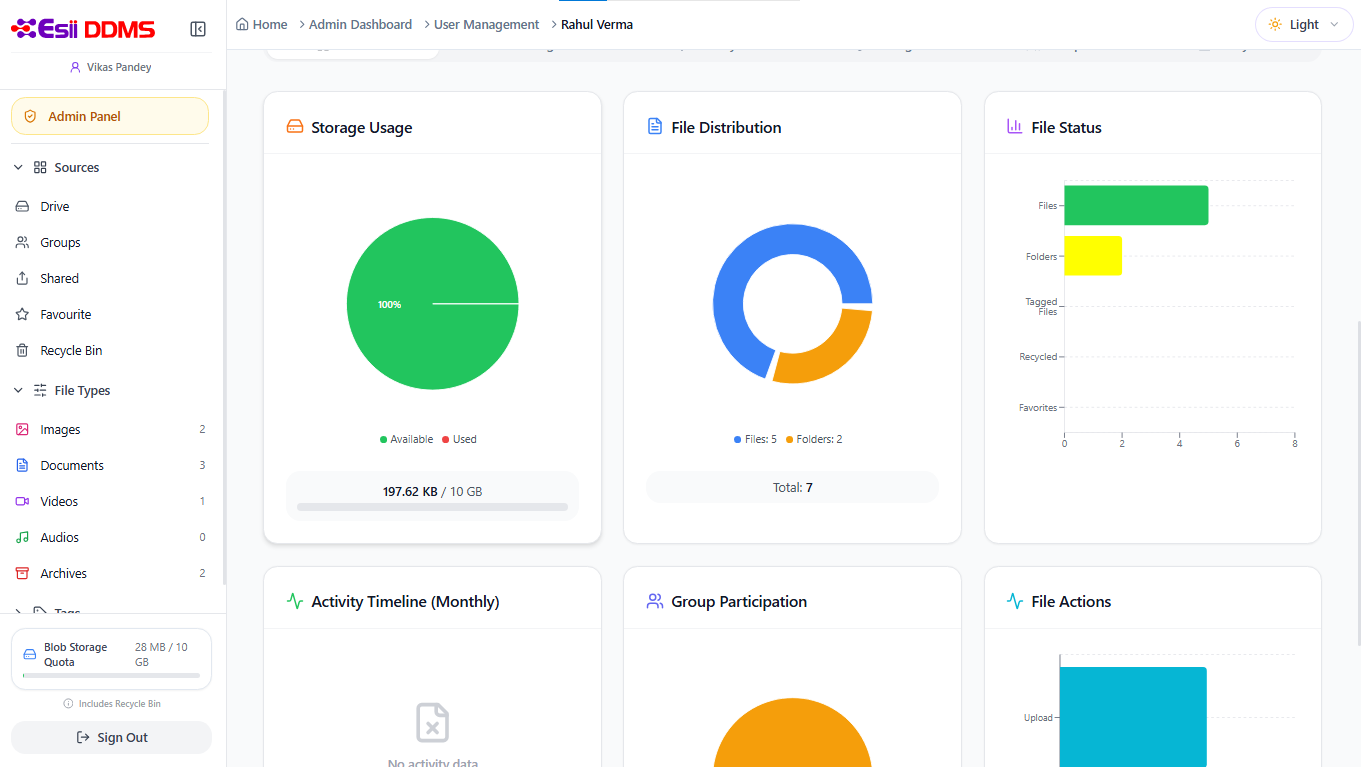
Edits, downloads and views trigger real-time notifications. Administrators always know what is happening to a document, not just who last touched it.
4. Share with a time-limited secure link
External sharing uses a time-limited, expiring link, regardless of which storage source the file lives on. Every access event is logged.
Built for the document realities of large enterprises.
DDMS is not a file-sharing tool. It is a governed document infrastructure.
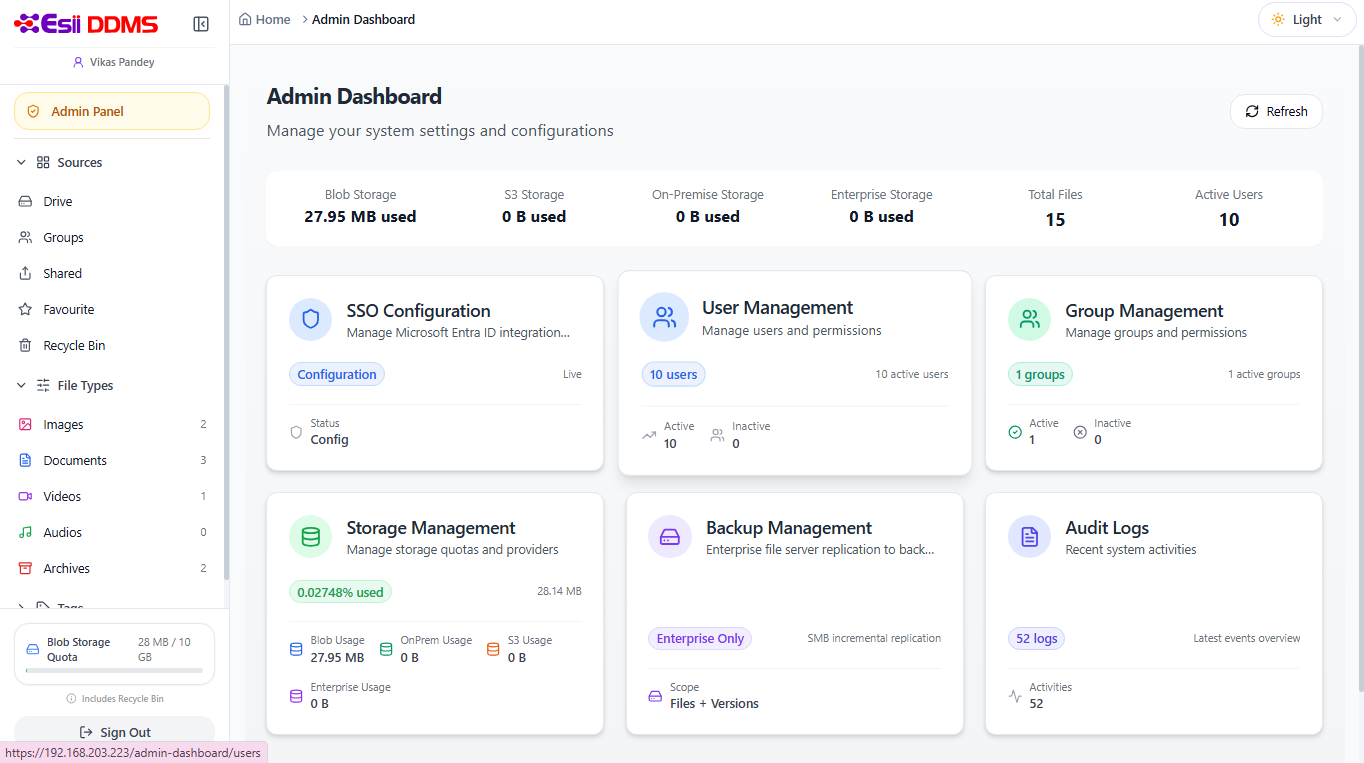
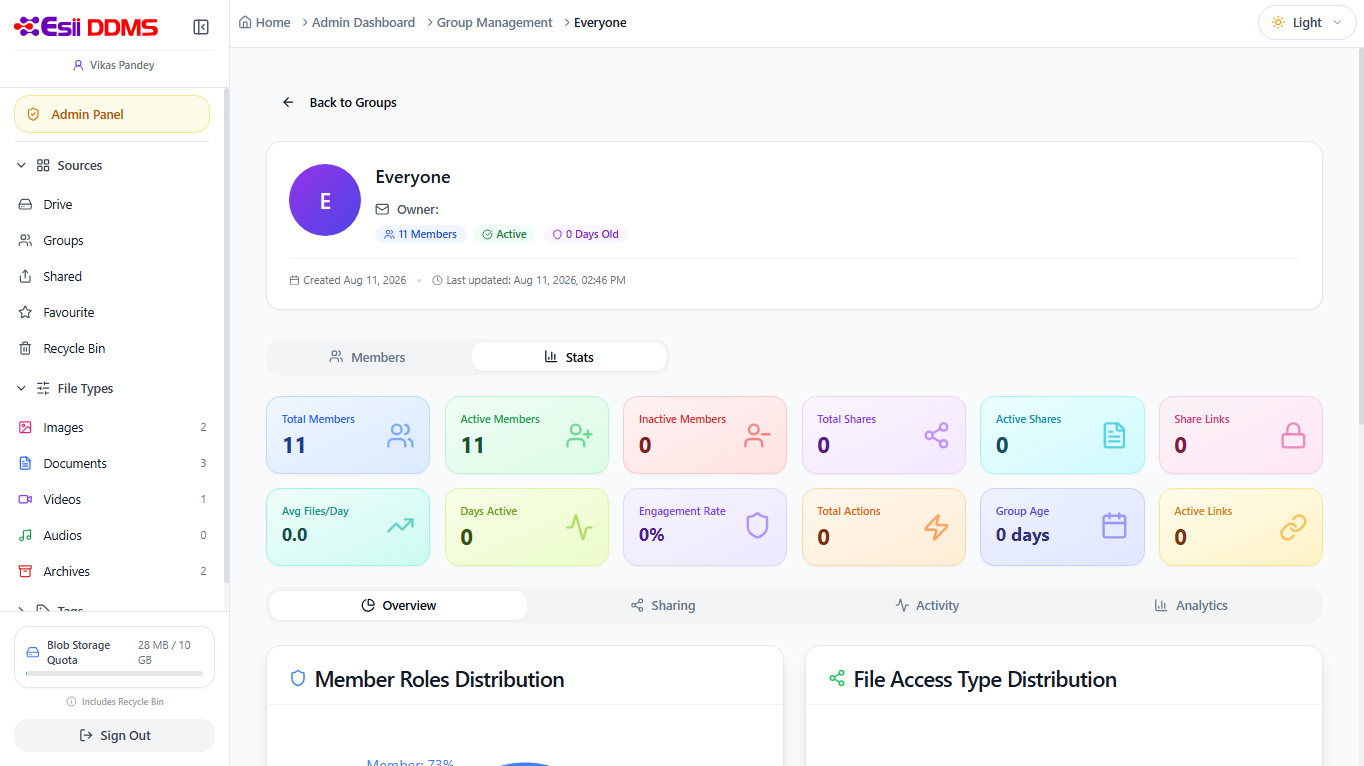
Granular RBAC ensures every user sees only what their role permits. Delegated permissions for department admins without IT involvement.
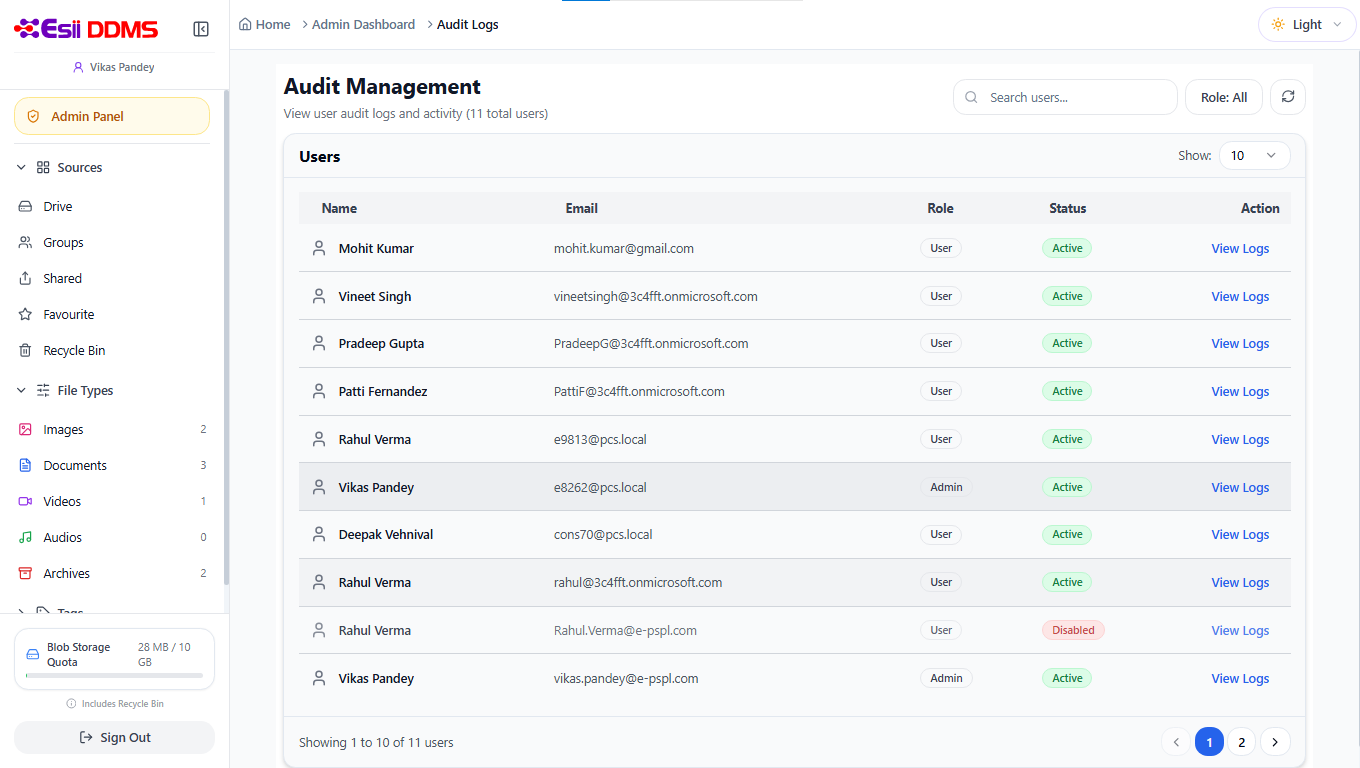
Every file activity is logged. Upload, view, download, share and delete. Full chain of custody for compliance and legal review.
Shared links expire automatically. Temporary SAS tokens ensure external parties cannot access files beyond the granted window.
Every file and folder action is tracked as it happens. Edits, downloads and views trigger real-time notifications to administrators.
Connects to NAS, AWS S3, Azure Blob, Windows File Server and Google Cloud Storage as they are. Data residency compliance without re-architecting.
Integrated file previews without downloading. Office documents handled via secure proxy. Search across metadata, tags and document content.
Use Cases
Where DDMS delivers immediate governance value.
DDMS is deployed across legal, finance, HR, procurement and operations functions.

Contracts and policy documents, controlled and versioned
Contracts and policy documents with controlled access and a complete version trail, on demand for any compliance review.

Financial reports shared through expiring links
Financial reports shared with external auditors through time-limited, secure links. Every access event logged.

SOPs managed as a living library
SOPs and process documents managed as a living library, with access controlled by role instead of by folder location.

Employee documents with department-level isolation
Employee documents stored with department-level isolation and compliance logging built in.
Connects to the storage and identity you already run.
No new storage infrastructure required, on any of these.


Bring governance to your enterprise documents.
We demonstrate DDMS on your document types and access structures. No data migration required to see the product.